Showing posts with label Cyberattack. Show all posts
Showing posts with label Cyberattack. Show all posts
Sunday, September 06, 2026


Saturday, August 15, 2026
Hackers Are Coming for Your Tap Water
A flurry of recent cyberattacks shows a new battleground for which local authorities are ill-prepared.

RAQUEL NATALICCHIO|HOUSTON CHRONICLE|GETTY IMAGES
A water tower is seen through a canopy of trees in Sugar Land, Texas.

By Olivier Knox
|
Aug. 11, 2026, at 4:00 p.m.
Our water is under attack.
Last week, the Clayton County Water Authority in Georgia announced it was investigating a cyberattack that disrupted its operations “as utilities nationwide are facing a growing number of cyber threats targeting critical infrastructure.”
The intrusion led to reduced water pressure in some areas, prompting CCWA to issue a boil-water advisory. Service was restored “within hours,” and the boil advisory was lifted after testing showed the water was safe to drink, it said.
Welcome to a relatively new national security cyber battleground. You’ve seen cyberattacks on businesses and the federal government before. But now it looks like malicious actors have turned their attention to the life-sustaining substance that comes out of your tap.
Saturday, August 01, 2026
Sunday, March 01, 2026
Strikes on Iran will test US cyber strategy abroad, and defenses at home
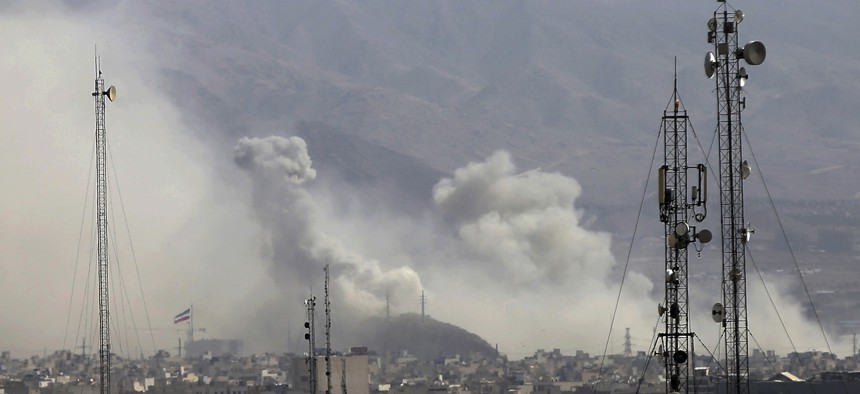
Smoke rises over Tehran after airstrikes on Iran on February 28, 2026. FATEMEH BAHRAMI/ANADOLU VIA GETTY IMAGES
The federal government’s cyber defense agency is short-staffed, and Tehran is known for its retaliatory cyberattacks.

BY DAVID DIMOLFETTA
CYBERSECURITY REPORTER, NEXTGOV/FCW
FEBRUARY 28, 2026 06:14 PM ET
Coordinated U.S. and Israeli strikes on Iranian targets are putting renewed focus on how the United States integrates offensive cyber capabilities into the battlespace — and how prepared federal agencies are for retaliation at home.
Iran has shown a tendency to respond to overseas threats with cyber means, from defacing websites to spying on U.S. and allied targets. Tracking such actions and alerting the U.S. government and public is a job of the Cybersecurity and Infrastructure Security Agency, which has been operating with sharply reduced staffing due to a funding lapse for its parent agency, the Department of Homeland Security.
“This is a bad time for Washington’s cyber agency to be operating with limited staff,” said Annie Fixler, director of the Center on Cyber and Technology Innovation at the Foundation for Defense of Democracies, a national security think tank.
That funding lapse comes after Trump-administration moves shrank CISA’s workforce by about one-third last year and degraded public-private collaboration mechanisms. This “limits the ability of the federal government to provide timely cyber threat information to the private sector,” Fixler said.
In the wake of the U.S. and Israeli airstrikes, American companies could see a “barrage” of low-level attacks like website defacements and distributed denial-of-service attacks, said Fixler. “Iran might also see some limited success against targets that do not have proper cyber hygiene — exposed edge devices with default passwords, for example.”
Other cyber experts said the U.S. should prepare for a mix of distributed denial-of-service campaigns, ransomware and hack-and-leak operations meant to send a message.
“While it’s not operating at the same technical level as China or Russia, Iranian-linked groups have carried out disruptive attacks against U.S. financial institutions, infrastructure providers and private sector companies,” said Tom Pace, a former Marine intelligence specialist and CEO of NetRise, a cybersecurity supply chain firm.
The conflict will likely see a surge in state-sponsored hacking activity, “specifically targeting operational technology and critical infrastructure through the exploitation of internet-facing industrial control systems and vulnerable [programmable logic controller] hardware,” said Brian Harrell, a former CISA official.
“Threat hunters should be working overtime right now. By combining disruptive attacks with psychological operations, Iran will seek to erode public trust in government institutions and project domestic strength during periods of heightened conflict,” he said.
Elisity CEO James Winebrenner echoed that advice. “We should be vigilant in protecting exposed [industrial controls systems] and expect heightened retaliatory activity in the coming days and weeks,” he said. In late 2023, Iran-linked hackers digitally defaced U.S. water treatment equipment.
Tehran may play up the effectiveness and scope of their cyberattacks, said Cynthia Kaiser, a former FBI cybersecurity deputy director who leads the Ransomware Research Center at Halcyon. Industry research has documented these theatrics.
“They’ll turn [an intrusion] into an information operation, and say, ‘Look, we compromised this entire facility,’ even though they compromised just a machine,” Kaiser said.
Sunday, August 20, 2023
Monday, March 14, 2022
Friday, October 21, 2016
WHAT WE KNOW ABOUT FRIDAY’S MASSIVE EAST COAST INTERNET OUTAGE

AUTHOR: LILY HAY NEWMAN.LILY HAY NEWMAN SECURITY
DATE OF PUBLICATION: 10.21.16.10.21.16
TIME OF PUBLICATION: 1:04 PM.1:04 PM
GETTY IMAGES
FRIDAY MORNING IS prime time for some casual news reading, tweeting, and general Internet browsing, but you may have had some trouble accessing your usual sites and services this morning and throughout the day, from Spotify and Reddit to the New York Times and even good ol’ WIRED.com. For that, you can thank a distributed denial of service attack (DDoS) that took down a big chunk of the Internet for most of the Eastern seaboard.
This morning’s attack started around 7 am ET and was aimed at Dyn, an Internet infrastructure company headquartered in New Hampshire. That first bout was resolved after about two hours; a second attack began just before noon. Dyn reported a third wave of attacks a little after 4pm ET, and called the overall situation a “very sophisticated and complex attack” stemming from tens of millions of IP addresses. In all cases, traffic to Dyn’s Internet directory servers throughout the US—primarily on the East Coast but later on the opposite end of the country as well—was stopped by a flood of malicious requests disrupting the system. Still ongoing, the situation is a definite reminder of the fragility of the web, and the power of the forces that aim to disrupt it.
Subscribe to:
Posts (Atom)