Showing posts with label theft. Show all posts

Sunday, September 13, 2026

Americans Are Stealing Food Now And Stores Are Locking Everything Up

Americans Are Stealing Food Now And Stores Are Locking Everything Up

Epic Economist

Sep 12, 2026

There are two separate things going on in this video, and it matters that they do not get blurred together. The first is what somebody says once they are caught. Hardly anybody argues they did not do it — they argue about what it was for, and the sentence that keeps surfacing is some version of I needed to feed my family. That may be true and it may be a line, and there is no way to tell which from the outside.

The second thing is not people at all. It is equipment. A camera counting you. A check at the door. A glass case you have to ring a bell for. All of it signed off as an answer to the first thing, and all of it landing on the ninety-nine who paid. That is the part nobody explained to anyone who shops in one of these stores, and it is the part this video is really about.

Monday, April 27, 2026

If You Can Keep It: What the wealth gap means for democracy

10:00 AM

If You Can Keep It: What the wealth gap means for Democracy 


Democratic New York City mayor Zohran Mamdani in the Brooklyn borough of New York City.
Stephanie Keith/Getty Images


A growing number of states are looking at implementing a wealth tax to fund social services.

California is among them, with a billionaire tax set to be included on its November ballot. And this month, New York City Mayor Zohran Mamdani, a democratic socialist, and Democratic New York Gov. Kathy Hochul introduced a proposed tax on luxury second homes in the city. In March, Washington passed its first ever income tax – which has already been met with a legal challenge.

All this comes as the wealth gap in the U.S. grows to its widest point in three decades – and only looks set to keep increasing. In this installment of “If You Can Keep It,” we look at how tax codes have contributed to a growing inequality in the country, how to fix it, and what this wealth gap means for the health of our democracy.


Guests

Ray Madoff
professor, Boston College Law School; author, "The Second Estate: How the Tax Code Made an American Aristocracy"

Kyle Pomerleau
senior fellow, American Enterprise Institute

Morris Pearl
chair, Patriotic Millionaires; former managing director, BlackRock; co-author, "Tax the Rich!"


Friday, April 24, 2026

The Minnesota Files: Unpacking the Bombshell Allegations of Medicaid Fraud and Political Power

Characters Charlotte Liam
Tháng Tư 23, 2026


In the rapidly evolving landscape of 21st-century media, the traditional gatekeepers of information are increasingly finding themselves challenged by an agile, technologically savvy force: the citizen journalist. Among this new vanguard of independent investigators stands Nick Shirley. His recent podcast revelation regarding the alleged misappropriation of billions in Medicaid funds in Minnesota has sent shockwaves through the political establishment, signaling a potential turning point in how constituents view the relationship between federal funding and local oversight.

According to Shirley, what began as a routine investigation into financial irregularities has morphed into a sprawling, high-stakes exposure. At the center of his allegations are two of Minnesota’s most prominent political figures: Senator Amy Klobuchar and Congresswoman Ilhan Omar. Shirley’s claims, characterized by their specificity and boldness, paint a picture of a calculated scheme, a “scam” that he asserts the perpetrators believed would remain forever buried beneath the bureaucratic layers of government.

This article explores the gravity of these allegations, the mechanism of the reported fraud, and the broader implications of Shirley’s findings for the current political climate.

Tuesday, March 17, 2026

FBI shuts down 3 India-based call centers posing as Social Security, tied to $50M stolen from Americans.


NBC 4 Washington


Here’s how they worked


Mar 2, 2026

A collaborative effort by the FBI, local police and Indian authorities has shut down a huge scam call center operation in India that saw Americans lose nearly $50 million.

The FBI Baltimore Field Office, Montgomery County Police Department and Montgomery County State’s Attorney’s Office announced that a coordinated investigation traced scams reported by Montgomery County, Maryland, residents to “extensive international scam call center operations in India that had been targeting Americans since 2022,” according to a news release (1).

The FBI says that about 660 people in the U.S. reported falling victim to government impersonation and tech support scams since 2022 that were connected to the call centers, with losses totaling a staggering $48,778,230. In Maryland alone, nearly two dozen victims reported losing a total of $6,257,869.

Behind those staggering figures are real people who believed they were protecting their savings — until it was too late. Their stories reveal what you can do to protect yourself.

Sunday, December 28, 2025

Indicted Democrat Editing Diamond Ring Out of Photo Raises Eyebrows

PUBLISHED
DEC 26, 2025, AT 03:28 PM EST

UPDATED
DEC 26, 2025, AT 03:29 PM EST

Florida Democrat Representative Sheila Cherfilus-McCormick has come under fire for allegedly editing out her diamond ring in a new holiday photo post shared on X.

Cherfilus-McCormick, 46, was indicted in November for allegedly stealing $5 million in FEMA coronavirus relief funds. The new post appears to have airbrushed out a $109,000 yellow diamond ring she’s accused of buying with the allegedly stolen cash.

Newsweek reached out to Cherfilus-McCormick for comment via email.

Why It Matters

A federal grand jury in Miami indicted Cherfilus-McCormick and several co-defendants in November, charging them with stealing roughly $5 million in Federal Emergency Management Agency disaster-relief funds. They are also accused of funneling the money into Cherfilus-McCormick’s 2021 congressional campaign, according to the U.S. Department of Justice.

Cherfilus-McCormick represents Florida’s 20th District. Her brother, Edwin Cherfilus, also was charged after allegedly diverting an overpayment from a COVID-19 vaccination-staffing contract to the family’s home health care business. Both have pleaded not guilty.


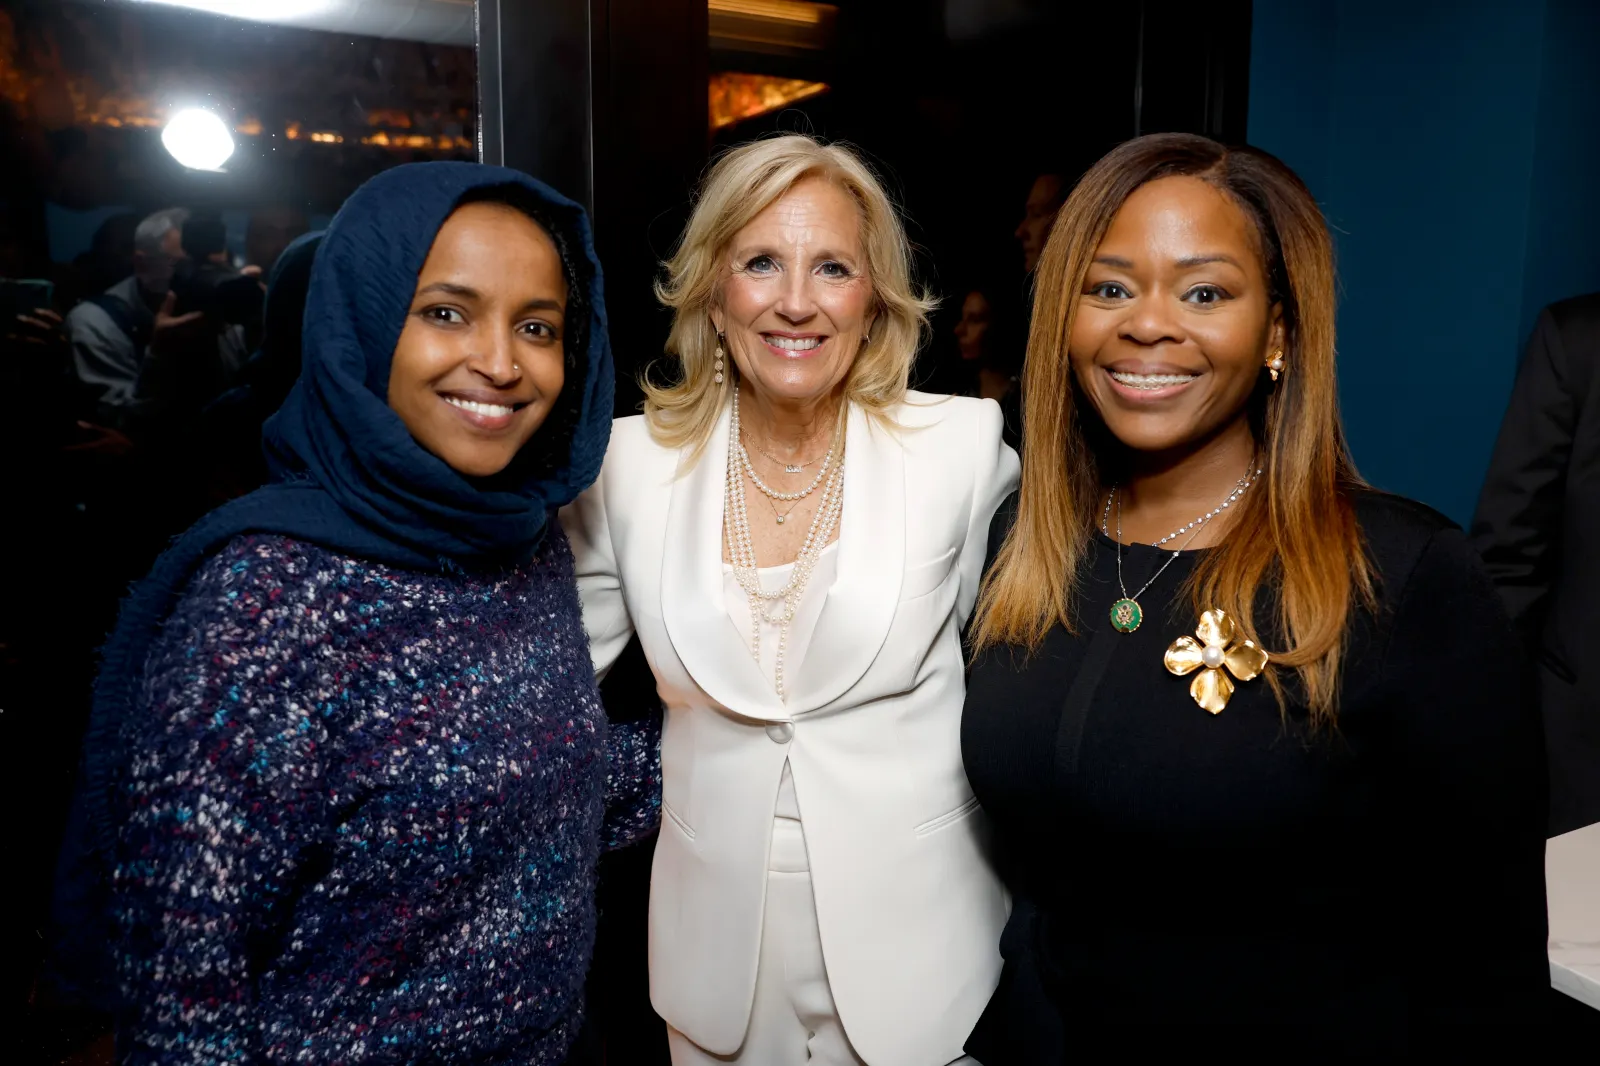
From left: Representative Ilhan Omar, then-first lady Jill Biden and Representative Sheila Cherfilus-McCormick attend the Women of Impact Celebration hosted by ELLE at Ciel Social Club on April 28, 2023, in Washington. (Photo by Tasos Katopodis/Getty Images for ELLE).

Wednesday, December 03, 2025

EXCLUSIVE: Somali Terrorists STOLE OVER $1 BILLION from Minnesota Taxpayers


EXCLUSIVE: Somali Terrorists STOLE OVER $1 BILLION from Minnesota Taxpayers


Rufo & Lomez and 2 more

Premiered Nov 21, 2025

Somalis in Minnesota are stealing BILLIONS in taxpayer cash and smuggling it to al-Shabaab terrorists. Why are Tim Walz and Democrats covering it up?

...

Saturday, December 02, 2023

Societal Malaise


Volume 42 Issue Twelve December 2023

Last Trumpet Ministries · PO Box 806 · Beaver Dam, WI 53916

Phone: 920-887-2626 Internet: http://www.lasttrumpetministries.org

“For if the trumpet give an uncertain sound, who shall prepare himself to the battle?” I Cor. 14:8


Societal Malaise

“And thou hast removed my soul far off from peace: I forgat prosperity. And I said, My strength and my hope is perished from the LORD.”

Lamentations 3:17-18

Reading the news can be quite exasperating. Those who set out to learn about current events will often find confusing headlines and mixed signals. For example, countless news stories are proclaiming that the American economy is surprisingly strong. This includes a November 3, 2023, piece by The Wall Street Journal with the headline, “The Improbably Strong Economy.” (1) The report notes that unemployment in the United States is low, average hourly earnings have been rising, and despite the many predictions from economists to the contrary, recession has been avoided in 2023. We’re even told that inflation is finally cooling down. (2) This all sounds like good news. Yet, the national mood in the United States tells a different story.

Despite the efforts of the mass media to convince us that everything is wonderful, the American populace remains unconvinced. A headline from CNN published on November 8, 2023, declares, “Americans think the economy stinks, but wages are up and so is spending. Economists and political strategists are baffled.” (3) The report goes on to cite a recent CNN poll that found 72 percent of respondents say “things in this country today are going badly.” Another poll from the New York Times and Siena College found that a mere 2 percent of respondents said the economy is excellent. (4) Why is there a disparity between what we are told by the media and how the American people feel? Is everything getting better and better every day as they suggest, or is the reality far different for people living in the real world?

One of the primary reasons the American people are so down on the economy is because of persistently high inflation. When inflation is high, it affects almost everything we buy. Every time we visit a supermarket, we’re reminded of the fact that we’re spending far more money on our groceries than we were three years ago. While reports indicate that inflation in October 2023 fell to only 3.2 percent, (5) the prices we pay still remain much higher than they used to be. In fact, the cost of groceries has risen on average by 25 percent since February 2020. (6)

One of the reasons economists say the economy is strong is because consumers have continued to spend gobs of money even as inflation remained stubbornly high. How is this possible? The American people have taken dramatic and sometimes desperate steps to maintain their standard of living. According to the Federal Reserve Bank of New York, Americans now owe a record-high 1.08 trillion dollars on their credit cards. (7) As credit card debt rises, the number of delinquent accounts is also increasing, which prompted The Wall Street Journal to report on November 25, 2023, “American borrowers are getting closer to maxing out.” The piece notes that households earning less than $50,000 per year with delinquent accounts are utilizing on average 80 to 90 percent of their available credit. (8) Thus, many who have been using credit cards to get by in recent years won’t be able to do this for much longer. Not only that, but getting new credit cards is becoming more difficult. “Tighter financial and credit conditions for households and businesses are likely to weigh on economic activity, hiring, and inflation,” the Federal Reserve said in a November 2023 statement. (9)

Tuesday, August 19, 2014

Hospital network hacked, 4.5 million records stolen

The Cybercrime Economy


By Jose Pagliery @Jose_Pagliery August 18, 2014: 3:25 PM ET


Hackers have taken 4.5 million Social Security numbers from patients who attended any one of Community Health Systems' 206 hospitals this year.

NEW YORK (CNNMoney)
Community Health Systems, which operates 206 hospitals across the United States, announced on Monday that hackers recently broke into its computers and stole data on 4.5 million patients.

Hackers have gained access to their names, Social Security numbers, physical addresses, birthdays and telephone numbers.

Anyone who received treatment from a physician's office tied to a network-owned hospital in the last five years -- or was merely referred there by an outside doctor -- is affected.

The large data breach puts these people at heightened risk of identity fraud. That allows criminals open bank accounts and credit cards on their behalf, take out loans and ruin personal credit history.

The company's hospitals operate in 28 states but have their most significant presence in Alabama, Florida, Mississippi, Oklahoma, Pennsylvania, Tennessee and Texas.

CNNMoney quiz: What hackers know about you

Community Health Systems (CYH) hired cybersecurity experts at Mandiant to consult on the hack. They have determined the hackers were in China and used high-end, sophisticated malware to launch the attacks sometime in April and June this year.

The FBI said it's working closely with the hospital network and "committing significant resources and efforts to target, disrupt, dismantle and arrest the perpetrators."

Federal investigators and Mandiant told the hospital network those hackers have previously been spotted conducting corporate espionage, targeting valuable information about medical devices.


.

Wednesday, August 06, 2014

Top gov't spyware company hacked; Gamma's FinFisher leaked


Summary: The maker of secretive FinFisher spyware -- sold exclusively to governments and police agencies -- has been hacked, revealing its clients, prices and its effectiveness across an unbelievable span of apps, operating systems and more.


By Violet Blue for Zero Day | August 6, 2014 -- 21:01 GMT (14:01 PDT)


The company that makes and sells the world's most elusive cyber weapon, FinFisher spyware, has been hacked and a 40G file has been dumped on the internet.

The slick and highly secret surveillance software can remotely control any computer it infects, copy files, intercept Skype calls, log keystrokes -- and now we know it can do much, much more.


A hacker has announced on Reddit and Twitter that they'd hacked Anglo-German company Gamma International UK Ltd., makers of FinFisher spyware sold exclusively to governments and police agencies.

The file was linked both on Reddit and "@GammaGroupPR" -- a parody Twitter account by the hacker taking credit for the breach. The Twitter account is still doling out tidbits from the massive theft.

The Reddit post Gamma International Leaked in self.Anarchism said,

Two years ago their software was found being widely used by governments in the middle east, especially Bahrain, to hack and spy on the computers and phones of journalists and dissidents.
Gamma Group (the company that makes FinFisher) denied having anything to do with it, saying they only sell their hacking tools to 'good' governments, and those authoritarian regimes most [sic] have stolen a copy.
...a couple days ago [when] I hacked in and made off with 40GB of data from Gamma's networks. I have hard proof they knew they were selling (and still are) to people using their software to attack Bahraini activists, along with a whole lot of other stuff in that 40GB.

The stolen FinFisher spoils were first leaked as a torrent file on Dropbox and have since been shared across the internet, meaning that controlling the information leak is now impossible.

FinFisher's notoriety of late has come from its use in the government targeting of activists, notably linked to the monitoring of high profile dissidents in Bahrain.

According to initial reports, the enormous file contains client lists, price lists, source code, details about the effectiveness of Finfisher malware, user and support documentation, a list of classes/tutorials, and much more.

One spreadsheet in the dump explains that FinFisher performed well against 35 top antivirus products, showing how the sophisticated malware efficiently defeats detection.

The documents also reveal usage statistics by country. 


The hacker posted to @GammaGrouPR:


A release notes doc covers Gamma's April 2014 patches to ensure its rootkit avoids Microsoft Security Essentials. It also explains that the malware records dual screen Windows setups, and reports better email spying with Mozilla Thunderbird and Apple Mail.

Gamma does note that FinFisher is detected by OSX Skype (a recording prompt appears), and the same is for Windows 8 Metro -- though the spyware goes well undetected by the desktop client.

The files also contain lists of apps the spyware utilizes, and things it can't use -- many still to be determined. There is a fake Adobe Flash Player updater, and a Firefox plugin for RealPlayer.

One of the files contains extensive (though still undetermined) documentation for WhatsApp.

Reporting on just such spyware last month, The Economist noted,

Currently it is legal for governments to buy the spyware—the sale and export of surveillance tools is virtually unregulated by international law.
Spyware providers say they sell their products to governments for “lawful purposes”.
But activists allege that their governments violate national laws in their often politically motivated use of such software. They argue that companies should be held accountable for selling spyware to repressive governments.

The Register reported:

A price list, which appeared to be a customers' record, revealed the FinSpy program cost 1.4 million Euros and a variety of penetration testing training services priced at 27,000 Euros each.
The document did not contain a date but it did show prices for malware targeting the recent iOS version 7 platform.

Links have appeared on Twitter to the GitHub repository for Finfisher docs, although it's being noted that due to Gamma's operational security practices, the unencerypted source code is fairly useless.

Gamma isn't in the business of creating zero-days because they are more of an "ecosystem" spyware company, but apparently they do sell it to their clients.

On the list of zero-day companies from which Gamma appears to purchase its exploits is the controversial French company, VUPEN.


The documents are going to give those fighting against Gamma, and trying to circumvent Finfisher spyware, an advantage that was previously unimaginable.

Special Feature

IT Security in the Snowden Era

The Edward Snowden revelations have rocked governments, global businesses, and the technology world. Here is our perspective on the still-unfolding implications along with IT security and risk management best practices that technology leaders can put to good use.

Read more


The docs will be of interest particularly to researchers at CitizenLab, who have been working to understand and reveal FinFisher (and its component Finspy) for the past few years.

CitizenLab released its first fill report on Gamma and FinFisher in a July 2012 post, From Bahrain With Love: FinFisher's Spy Kit Exposed?

Bloomberg detailed the efforts to unmask the spyware inCyber Attacks on Activists Traced to FinFisher Spyware of Gamma, saying:

For the past year, human rights advocates and virus hunters have scrutinized FinFisher, seeking to uncover potential abuses. They got a glimpse of its reach when a FinFisher sales pitch to Egyptian state security was uncovered after that country's February 2011 revolution.

Until then, researchers had only suspected the malware's existence. Mikko Hypponen, chief research officer at Helsinki-based security company F-Secure, told Bloomberg at the time, "We know it exists, but we've never seen it -- you can imagine a rare diamond."

It's safe to say that we're going to be finding out a lot more in the weeks to come about this previously well-kept spying secret.

    S

    Friday, January 10, 2014

    Internet Criminals Stole a Half Million Dollars from the Seventh-day Adventist General Conference


    By AT News Team, January 6, 2014

    Last week the General Conference of the Seventh-day Adventist Church released a statement that it had been the victim of online theft. No personal information was taken, but about $500,000 was stolen, according to the statement released by Adventist News Network (ANN), the official news service of the denomination.

    The theft involved a transfer of funds for an organization or institution within the denomination. Church officials are cooperating with Federal authorities in the United States who are investigating the crime. They are also working with the banks and insurance companies to determine what recoveries may be possible. Information so far suggests that there was no insider involvement in the crime.

    “No personal information such as private information, personal donor records or internal accounts were accessed or compromised in the scheme” assured the denomination's treasurer, Bob Lemon. “We are modifying procedures to do our best to prevent this from happening again.”


    Source
    .
    .
    .

    Thursday, June 06, 2013

    Global cybercrime ring targeted by Microsoft and FBI


    Microsoft teamed up with the FBI to disrupt armies of hacked computers used to commit more than a half-billion dollars in financial fraud around the world, it claimed yesterday


    Nearly 20m pieces of personal information were illegally sold online in the first six months of the year Photo: GETTY IMAGES


    By PA

    9:14AM BST 06 Jun 2013


    A strike coordinated with police and financial institutions disabled more than a thousand "botnets" used by a global cybercrime operation to steal people's banking information and identities, according to the software colossus.

    Botnets are networks of computers infected with viruses that let them be controlled by hackers.

    "Crimes used to happen through stickups, but today criminals use mouse clicks," said former US Department of Homeland Security cyber official Greg Garcia, a consultant who spoke for financial industry associations. "This action aims to stop the ongoing harm of these Citadel botnets against people and businesses worldwide."

    An investigation launched early last year led Microsoft and its allies to malicious software called Citadel, which monitors keystrokes on infected machines and sends information such as account names and passwords to hackers.

    Cybercriminals used stolen passwords to take money from online bank accounts, according to Microsoft.


    .
    .
    .

    Wednesday, May 29, 2013

    Boston church official pleads not guilty to racketeering, extortion, conspiracy charges


    Published May 28, 2013

    Associated Press


    BOSTON – A Boston church official who claimed in an autobiography that he was a leg-breaker for reputed gangster James "Whitey" Bulger has pleaded not guilty to charges that he looted the church's assets.

    Edward MacKenzie Jr. is the former director of operations at the Boston Society of the New Jerusalem Church, whose members belong to the Swedenborgian denomination.

    MacKenzie was arrested last week after a grand jury indicted him on charges including racketeering and extortion.

    Federal authorities say MacKenzie looted the church of its considerable financial assets through fraud, deceit, extortion, theft and bribery.

    MacKenzie pleaded not guilty Tuesday to all 14 charges against him. Each count carries a maximum 20-year sentence.

    His bail hearing was postponed until June 26 after a new defense attorney requested more time.


    Source: http://www.foxnews.com/us/2013/05/28/boston-church-official-pleads-not-guilty-to-racketeering-extortion-conspiracy/#ixzz2UcvQ8Qkb
    .
    .

    Thursday, April 04, 2013

    ALERT: All Of The Money In Your Bank Account Could Disappear In A Single Moment


    Posted on April 3, 2013 by Michael Snyder


    What would you do if you logged in to your bank account someday and it showed that you had a zero balance and your bank had no record that you ever had any money in your account? What would you do if all of the money in your bank account suddenly disappeared in a single moment? If you had not kept any paper records, which most Americans do not, it would be exceedingly difficult to prove to the bank that you actually had any money in the bank. If you don't think that something like this could ever happen in the United States, you might want to think again. Cyber attacks against major banks in the United States are becoming more powerful and more sophisticated with each passing month. In fact, major U.S. bank websites have been offline for a total of 249 hours over the past six weeks. And just last month, thousands upon thousands of Chase customers logged into their bank accounts only to discover that their balances had all been reset to zero. Anyone that would want to cause complete and total economic chaos in the United States could accomplish it very easily by wiping out all of our bank account records. So please do not keep all of your money in a single bank, and from now on please keep a paper copy of all of your bank account statements. At some point it is likely that one of these cyber attacks will cause permanent damage to our banking system, and you want to be protected.

    The mainstream media has generally been very quiet about the massive cyber attacks against our major banks, but behind the scenes authorities are truly alarmed. They don't know how to stop these attacks, and they just keep getting more intense and more sophisticated.

    Could you imagine how you would feel if you logged in to your bank account and all of your money was gone? That is exactly what happened to some Chase customers last month. The following is from a recent CNET article...

    JP Morgan Chase denied this evening that it had suffered a hack that many customers claimed had suddenly reduced their checking account balances to zero.

    After discovering the apparently empty accounts via the Internet or mobile devices, many Chase banking customers turned to Twitter to express their frustration and show screen shots of zero balances. Other users were greeted with messages that their bank account balances were unavailable.

    But this was most definitely not an isolated incident. That same article noted that Chase and many of our other large banks have had their websites taken down for extended periods of time lately...


    Customers' suspicions about a possible security breach are natural, with the zero balances appearing less than a week after a massive distributed-denial-of-service attack rendered Chase's Web sites useless for many hours. Customers trying to use the site's tools were instead greeted with a note that the site was "temporarily down."

    Hackers have ratcheted up their assaults on financial institutions in recent months, using DDoS attacks to take down Wells Fargo, Bank of America, Chase, Citigroup, HSBC, and others.

    In fact, as I mentioned above, major U.S. bank websites have been offline for an astounding 249 hours over the last six weeks alone. The attacks just keep getting larger and bank officials are becoming very alarmed about the power of these cyber attacks. The following is from an article that was posted on CNBC this week...


    Major U.S. bank websites have been offline a total of 249 hours in the past six weeks, perhaps the clearest indication yet that American companies are prime targets in an unrelenting, global cyber conflict.

    The heavier-than-usual outages are the result of a remarkable, sustained attack that began seven months ago and repeatedly knocks banks offline for hours at a time, frustrating consumers and bank security professionals alike.

    "Literally, these banks are just in war rooms, sitting at controls trying to stop (the attacks)," said Avivah Litan, a bank security analyst with Gartner Group, a consulting firm. "The frightening thing is (the attackers) are not using as much resources as they have on call. The attacks could be bigger."

    So who is behind these attacks?

    Some are blaming Chinese hackers, others believe that Iran is behind the attacks, and yet others are convinced that it is the work of Islamic terrorists.

    It is kind of frightening that they cannot positively identify who is behind these attacks. Whoever it is, they sure do seem to have a tremendous amount of resources and they are very sophisticated.

    And in the future, it may not be hackers on the other side of the globe that are attacking our banks. In fact, if someone wanted to "recapitalize the banks", all they would have to do is wipe out all of our bank account records (including all backup records). Suddenly trillions of dollars of "unsecured liabilities" (that is what our bank accounts are) would be wiped out and the banks would suddenly be solvent again. Anyone that could not produce evidence that they actually had money in the banks would be in a lot of trouble. It would be the largest single wealth transfer in the history of the world, and it would throw the U.S. economy into utter chaos. This is a scenario that I am exploring in my new novel which will be coming out later this month.

    And of course another way that your bank account could be wiped out in a single moment is if the government decides to "legally" steal it. We just witnessed this happen in Cyprus. In February, the Central Bank of Cyprus swore that such a thing could never possibly happen, but then one month later it did happen. The politicians will lie to your face until the very day comes when they steal your money.

    Sadly, a very similar thing could easily happen in the United States someday. As I wrote about yesterday, the big banks are making incredibly reckless bets with our money. When those bets go bad, our money could very well be used to cover those bets.

    One way this could be accomplished is by using a practice known as "rehypothecation". It sounds complicated, but it really isn't. Basically, the banks use money that clients have entrusted to them to cover their own gambling debts. This is how rehypothecaton is defined by Investopedia...


    "The practice by banks and brokers of using, for their own purposes, assets that have been posted as collateral by their clients."

    An excellent article by Jeff Nielson detailed how this could result in the big banks grabbing our money when their trillions of dollars of reckless bets go bad...


    1) Our banking regulators knowingly allow financial institutions to engage in recklessly misleading (if not outright fraudulent) contracts with their clients, through the use of complex “small print” in their account contracts with clients.

    2) The three largest U.S. “banks” by deposit (JP Morgan, Bank of America, Citigroup) have made bets in their own rigged casino, which total well in excess of $100 trillion, an amount which completely dwarfs their total, combined deposits (and assets).

    3) A large portion of those bets occur in the $60+ trillion credit default swap market. Pay-outs in these markets can (and do) exceed 300 times the amount of the original bet. It is bets in this market which “blew up” AIG, requiring more than $150 billion in immediate government aid.

    4) Following the Crash of ’08; these same banks mooched a package of hand-outs, tax-breaks and “guarantees” (i.e. future hand-outs) from the Bush regime in excess of $15 trillion, the last time their gambling debts went bad on them – and all of these banks have been allowed to dramatically increase the total amount of their gambling since then.

    5) It would take only a minor change in the gambling contracts in which these bankers engage to allow their creditors to seize funds out of ordinary bank accounts.

    6) The existing language for the bank accounts of these U.S. banks is possibly already so vague (and prejudicial to clients) that it would allow these banks to reinterpret the terms of these bank accounts – and allow rehypothecation to be used to rob the holders of ordinary bank accounts, people who themselves make no “bets” in markets whatsoever. Alternately, customers could be blitzed with an offer for “new and improved” bank accounts, where terms allowing rehypothecation are slipped into the contract, with the banks knowing that the “regulators” will do nothing to warn account-holders of the gigantic risk they are taking.

    But we are all covered by deposit insurance, right?

    That is what the people of Cyprus thought too.

    As we just saw in Cyprus, when there is a "banking crisis" sometimes government steps in and suddenly changes all of the rules overnight even though the vast majority of the population is against it.

    Hopefully you can see that no bank account will ever truly be "safe" ever again.

    Your money may be safe today, and your money may be there next week, but someday it could disappear in a single moment.

    And the general public is definitely starting to lose faith in the banking system. Google searches for the term "bank run" have been absolutely spiking recently. Just check out this chart which shows that searches for "bank run" are now the highest that they have ever been.

    So what should we all do to protect ourselves?

    As I mentioned earlier, it is important to not have all of your money in one bank, and from now on you will want to permanently keep paper copies of all of your bank account statements.

    Someday you may need those statements in order to prove that you actually had money in the bank.

    Our world is becoming increasingly unstable, and at some point financial disaster is going to strike.

    By taking prudent precautions now, hopefully you will be able to minimize the damage to your family.


    About Michael Snyder

    Michael Snyder is the editor of The Economic Collapse Blog


    .

    Could the U.S. Do Like Cyprus and Seize Bank Deposits?


    by John Grgurich, Apr 3rd 2013 4:30PM


    Getty Images


    Just when we all thought it was safe to stop worrying about the eurozone, another country's banking system blew up and stopped the Continent in its economic tracks.

    This time, the victim was Cyprus: a tiny Mediterranean island not far from Greece, whose two biggest banks were facing insolvency if Europe didn't come to the rescue. And yes, a last-minute rescue plan was arranged. But rather than simply bailing out the banks with EU taxpayer money, as had been done previously, the European Union initially decided to "bail in" the creditors -- that is, make people with money deposited in the banks take some of the hit for the rescue.

    Initially, part of this hit was going to be against insured depositors -- ordinary savers whose accounts were insured by the European Union up to €100,000. Had the plan gone through as proposed, they would have faced a one-time 6.75 percent tax on their accounts.

    However, there was such local and international uproar against the notion that ordinary citizens could have their bank accounts raided by the government that a new bailout plan was devised. This one protected insured depositors but still left those with various levels of "unsecured debt" -- i.e., very large deposits -- in the country's two biggest banks on the hook.

    The mere fact that Cyprus attempted to raid insured accounts has left a bad taste in people's mouths around the world. And it has led some people to ask: Could that ever happen here in America?

    Let's play pretend with the U.S. banking system

    Imagine if the U.S. found itself in Cyprus' situation, with a failing banking system and no way to save it except by accepting the terms of whatever rescue plan was handed down by foreign governments or multinational organizations.

    Finding that hard to imagine? It's no wonder.

    That's because, unlike EU members, Washington isn't subject to any superseding government. No outside force can dictate terms to it. And if the U.S. banking systemdoes get itself into trouble (as it did in when the housing bubble burst and tanked the markets), we're still not in danger of running out of money to pay off our IOUs.

    Unlike eurozone nations, we have our own currency. We can just "print" more of it until our debts are covered. So you can rest assured -- if the government needed money to prop up endangered banks, it surely wouldn't need to reach into your savings account to find it.

    True, there are dangers associated with flooding the market with dollars, inflation being one of them. But the fact remains that the U.S. literally can't run out of money. For Cyprus, and other countries that have had to take European Union bailout money because there was no other place to turn, this is one of the major downsides of not having a separate currency.

    Our ability to print money isn't the only stop-gap against a Cyprus situation. We also have a long-standing deposit-insuring agency: the Federal Deposit Insurance Corp.

    We've Got You Covered

    The FDIC was established as part of The Banking Act of 1933, in part as a response to the thousands of bank failures that occurred in the U.S. in the late 1920s and 1930s. (At FDIC-approved financial institutions, single depositors are covered up to $250,000 per owner, joint depositors are covered up to $250,000 per co-owner, and even IRAs are covered up to $250,000 per owner.)

    No depositor has ever lost a dollar on insured deposits under the limits since the depositor guarantee was written into law in 1933. Without first changing the law, no American president or other member of the federal government could unilaterally tax the accounts of insured bank depositors to "bail in" failing banks. (Interestingly, the FDIC and the Bank of England have floated the idea of a policy that could, in theory, legalize such bank account haircuts, turning the Cyprus experiment into a U.S. precedent. But at this point, it's only a White Paper, an ivory tower exercise.)

    And if you think there was an uproar over Cyprus trying a move like this, imagine the uproar the American press or Rep. Nancy Pelosi would create in response to a similar move.

    We've Got a Well-Established Blueprint

    The European Union and corresponding eurozone haven't been around for that long. There isn't much history in the eurozone as an entity, and the economic rule of law is still shaky in some of these smaller countries, like Cyprus.

    Since the financial crisis, they've been putting out fires left and right on a case-by-case basis with varying levels of consistency and success. And that's what the Cyprus rescue was: a poorly thought out, ad hoc response that panicked markets and citizens everywhere.

    Luckily for us in the U.S., we have history and established laws on our side. These two things, along with the flexibility having a separate currency provides, is why what happened in Cyprus can't happen here.

    John Grgurich is a regular contributor to The Motley Fool. Follow his dispatches from the bleeding heart of capitalism on Twitter @TMFGrgurich.


    Tuesday, April 02, 2013

    Tax on Deposits Means Stealing Your Money - Gerald Celente


    Greg Hunter

    Published on Mar 31, 2013

    http://usawatchdog.com/u-s-provoking-... Gerald Celente of The Trends Journal.com says the Cyprus banking crisis is coming to America. Celente explains, "Tax on deposits? Can any adult say stealing your money?" What about the recent lackluster performance of gold and silver? Can it still protect you? Celente says, "Suppose you can't get your money out of the banks. Suppose they just screwed you. You need food or fuel. You'd like a couple of pieces of gold or silver in your hand. You think that would buy you anything?" On the subject of Homeland Security stockpiling hollow point ammunition, Celente says, "That we are even having this discussion shows how fascist things have become. How much of history has to be repeated before we see it is repeating itself, again?" Join Greg Hunter as he goes One-on-One with Gerald Celente Publisher of the Trends Journal
    .